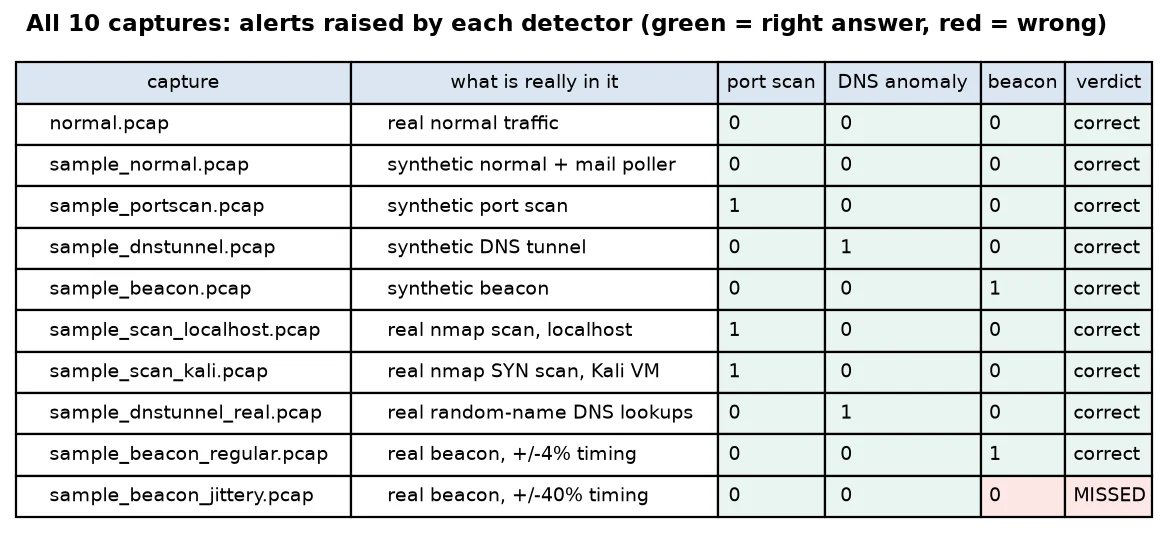
Wrote three Scapy detectors and tested them on synthetic captures and on real ones: nmap scans of my own computer and of a Kali VM on an isolated network, random-name DNS lookups, a timed beacon program, and five minutes of normal traffic.
HOW IT WORKS
01
Capture
Record real traffic from my own machines, and build synthetic captures with known contents.
02
Detect
Flag port scans, DNS tunneling, and beaconing with simple, explainable rules.
03
Check
Compare against Wireshark, measure the margins, and show where the rules fail.
WHAT I DELIVERED
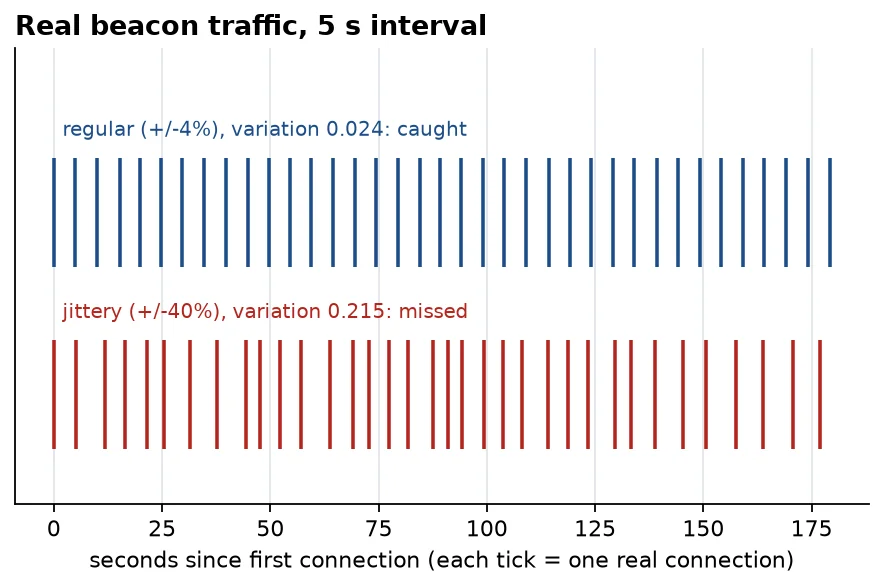
Each detector caught its attack in synthetic and real captures, except one real beacon with 40% timing jitter, and none fired on 5 minutes of real normal traffic (12,340 packets).
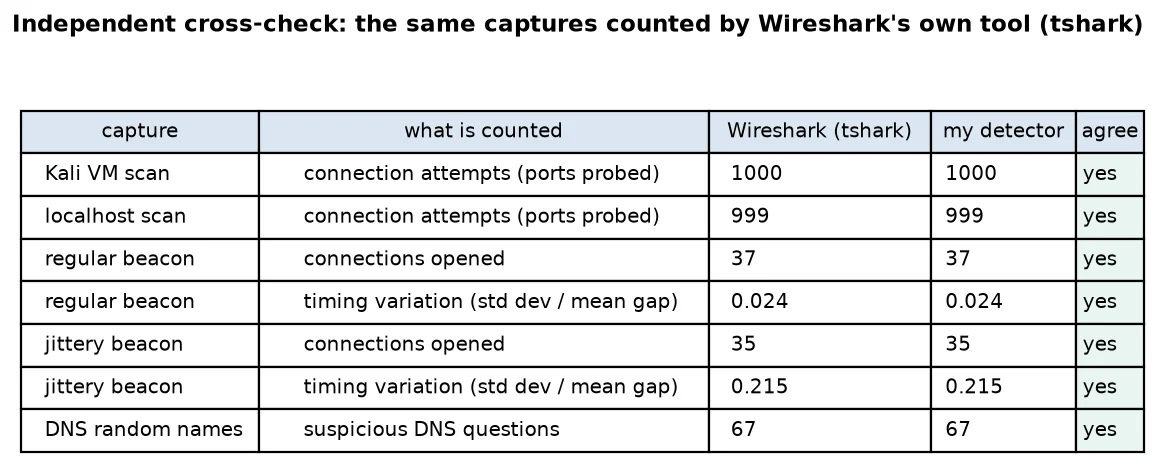
Cross-checked the counts against Wireshark’s tshark, and every figure matched.
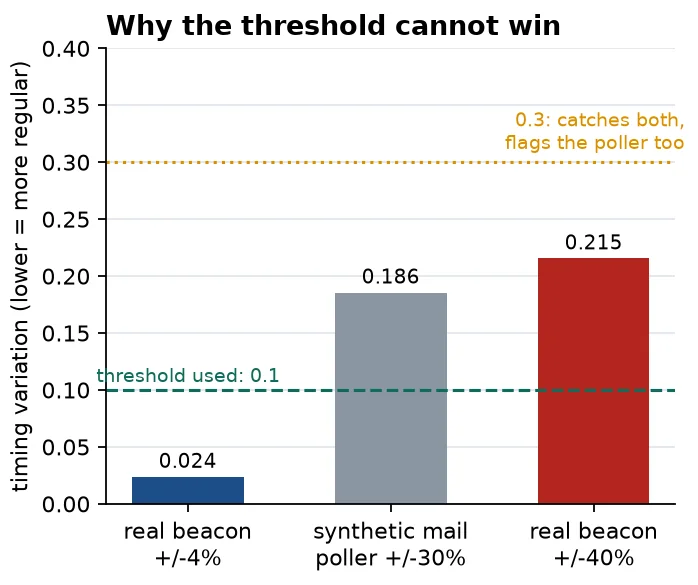
Documented the miss: loosening the beacon rule enough to catch the 40% jitter beacon also flags a simulated mail poller with 30% jitter.
Reported how close normal traffic came to each threshold, since zero alerts alone means little.
 (opens in a new tab)
 (opens in a new tab)
 (opens in a new tab)