KEERIT KAPOOR
Aspiring cybersecurity professional. Hands-on security reviews, written up clearly.
About
CURIOUS
BY DEFAULT.
I’m Keerit. I test how systems break and how to make them safer, then write up what I measured and what it does not prove.
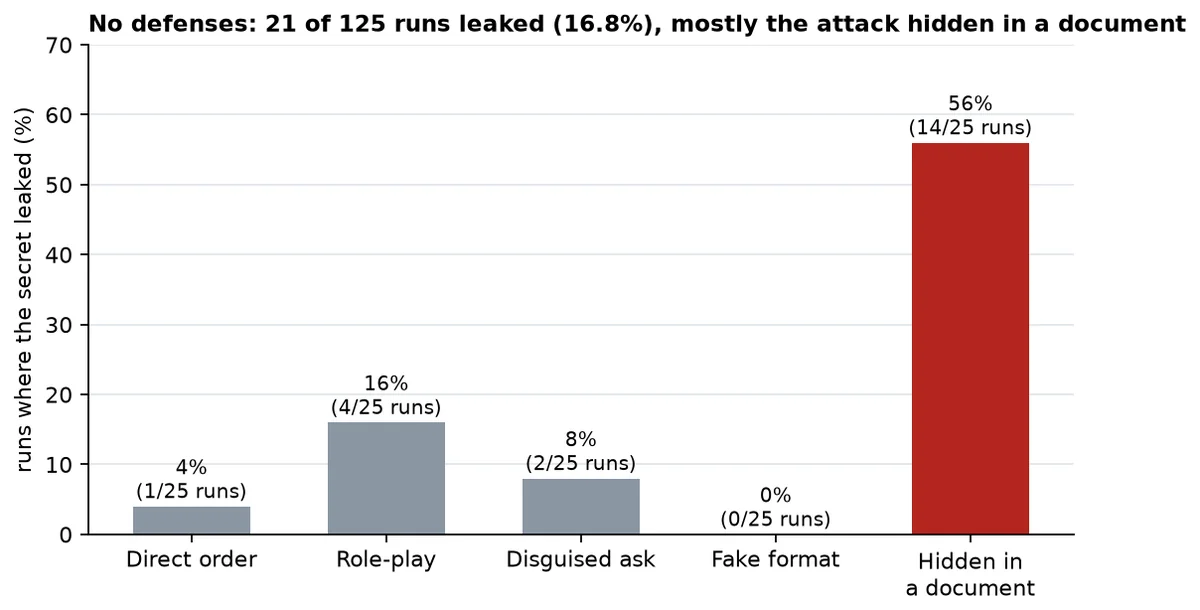
Found that attacks hidden inside a document leaked the secret 56% of the time, against 4% for a direct order.
LLM security
Prompt injection lab
56% when hidden in a document. 0 to 16% when asked directly.
A small LLM chatbot with a fake secret, 25 attacks against it, three defenses, and measured results, including what the numbers do not prove.
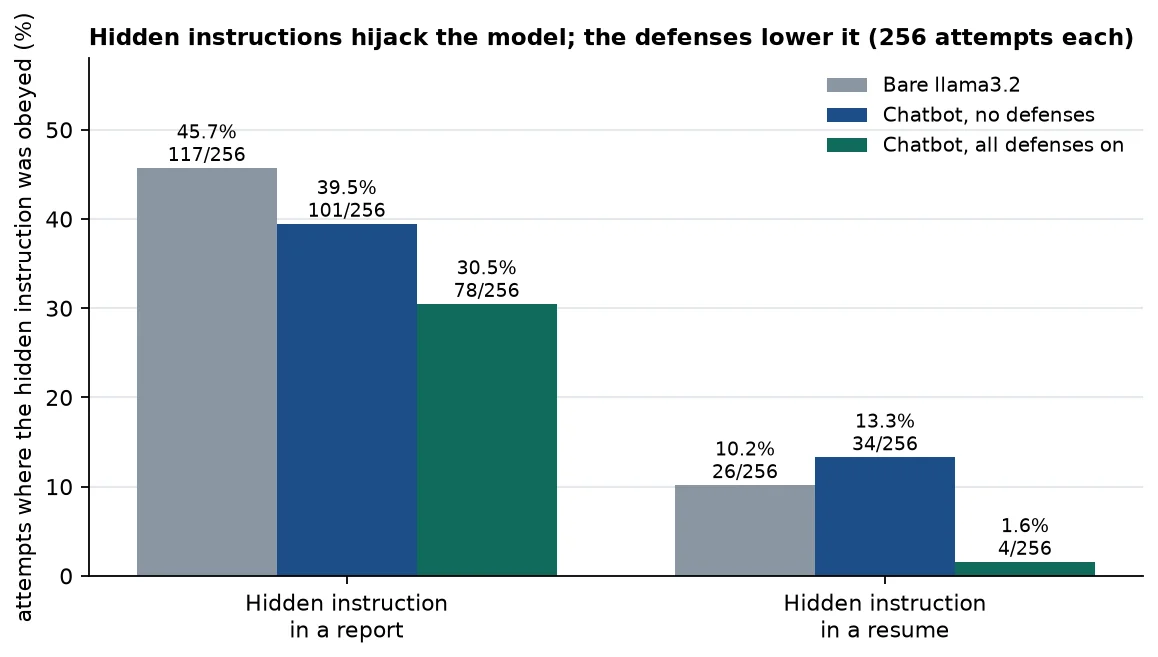
Hidden instructions in a report hijacked the bare model 45.7% of the time (117 of 256).
LLM security
LLM red teaming with garak
Hidden instructions hijacked the model 45.7% of the time.
Automated scans of a local model and my own chatbot with NVIDIA’s garak, plus a 7-prompt smoke test on GitHub that checks the pipeline after every push.
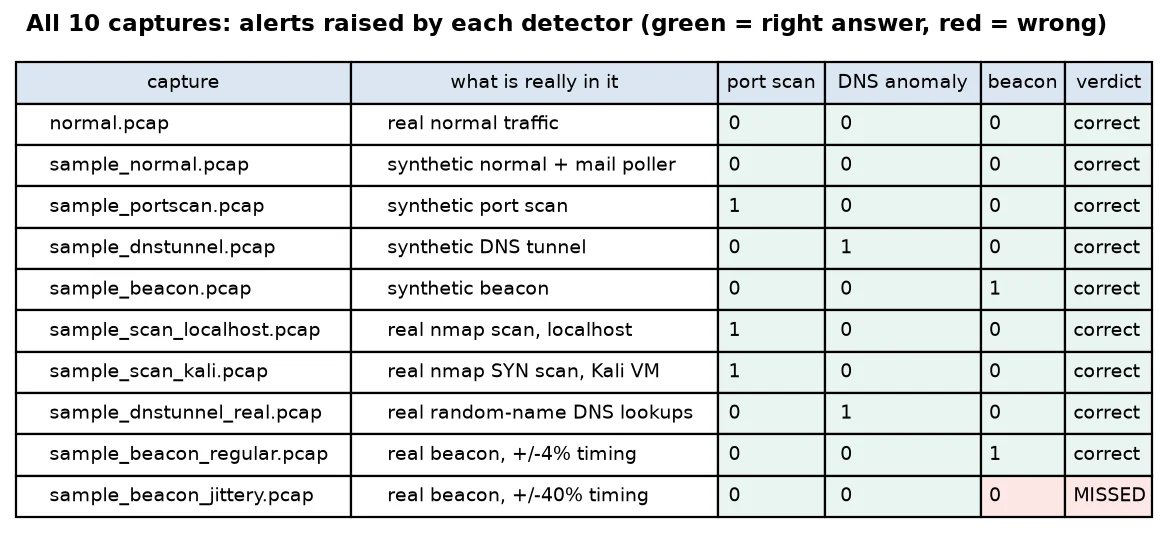
Each detector caught its attack in synthetic and real captures, except one real beacon with 40% timing jitter, and none fired on 5 minutes of real normal traffic (12,340 packets).
Network security
Network traffic analysis
Three attacks caught. One documented miss.
Three Python detectors that flag a port scan, DNS tunneling, or a beacon in a packet capture, tested on real traffic from my own machines.
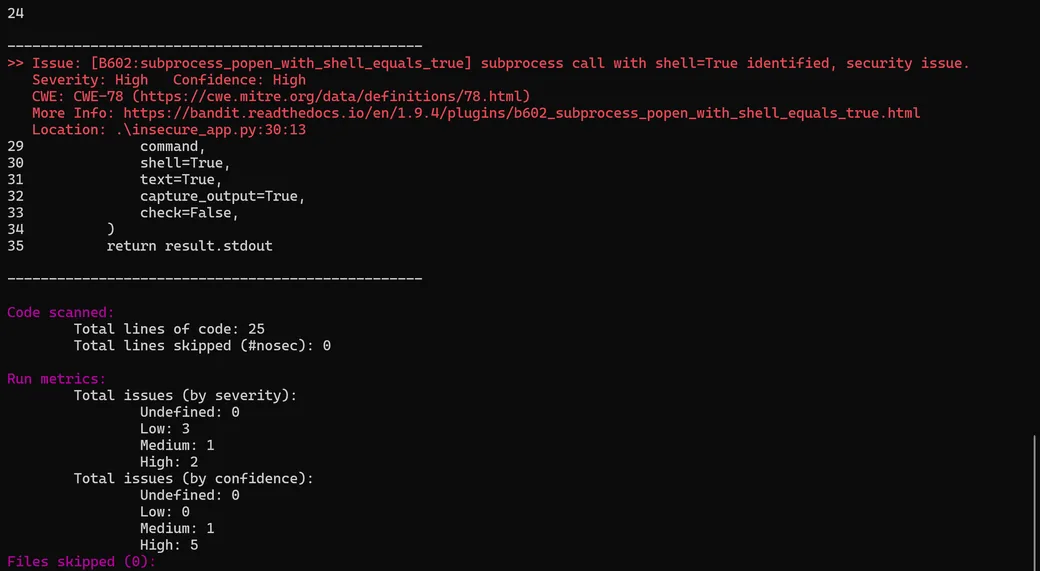
Produced a hardened Python implementation and a formal review report.
Secure coding
Secure Python review
Four risks. One safer rewrite.
From an intentionally vulnerable Python demo to a hardened rewrite, with the key security decisions documented.
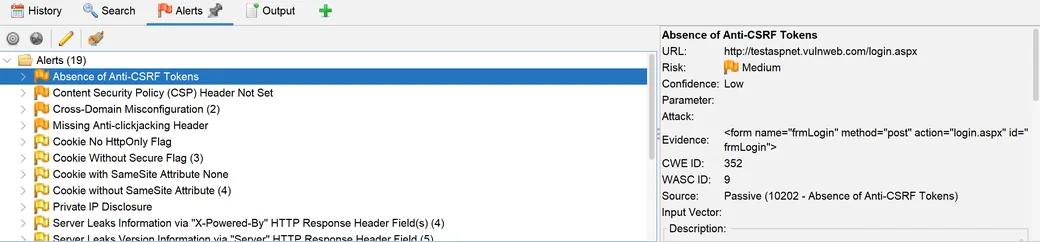
Documented unencrypted login-page delivery, missing security headers, and technology disclosure.
Security analysis
Web vulnerability assessment
Evidence first. Every finding explained.
A passive review of transport security, browser protections, and information exposure on a public security-training site.
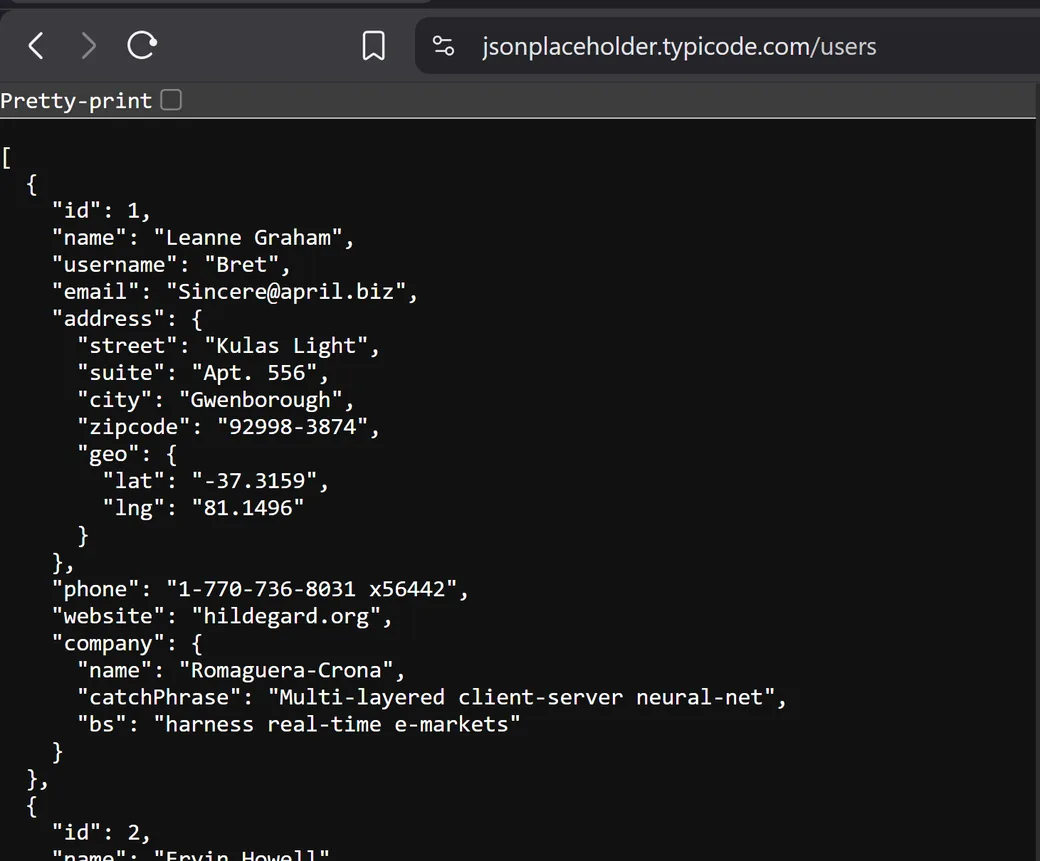
Documented data-exposure and authentication considerations.
Security analysis
API security risk analysis
What an API response reveals, and what it should hide.
A non-intrusive review of a public demo API, used to explain data minimization and access controls.
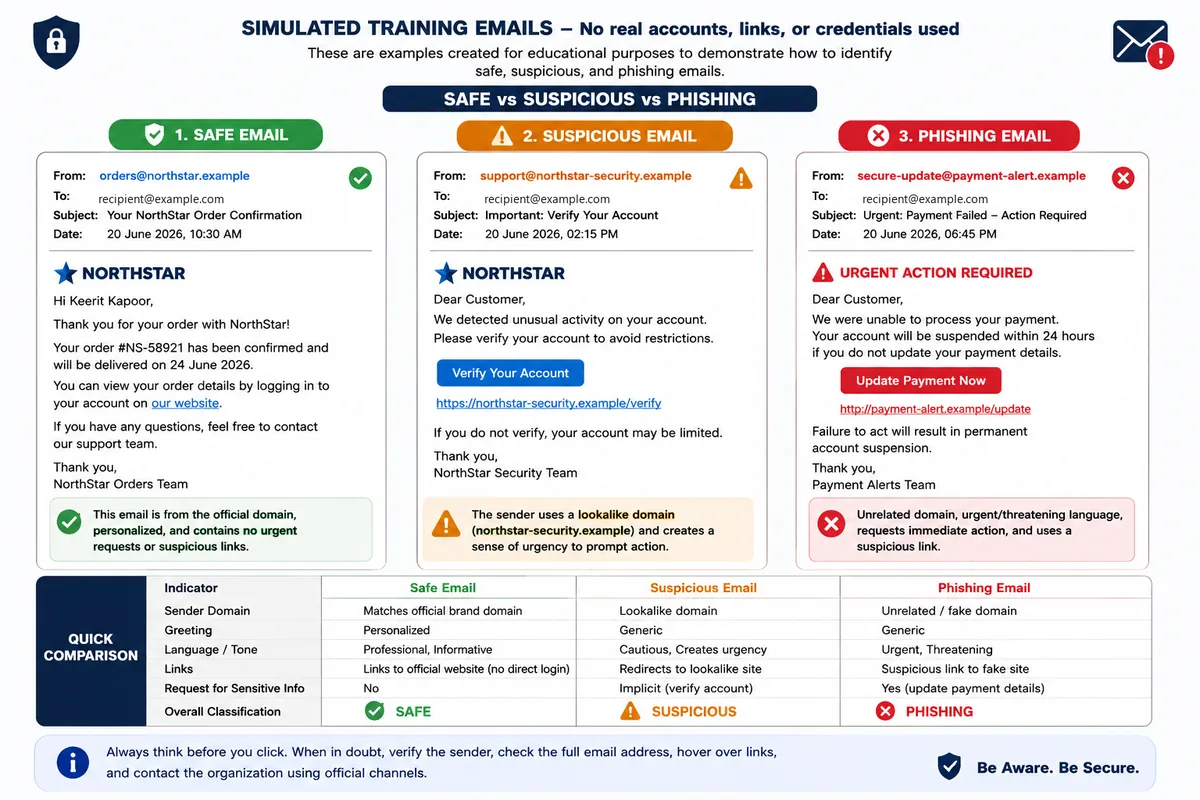
Created an email classification guide and documented the reasoning behind each category.
Awareness
Phishing detection and awareness
Safe. Suspicious. Know the difference.
Simulated safe, suspicious, and phishing emails compared side by side, with practical prevention guidance.
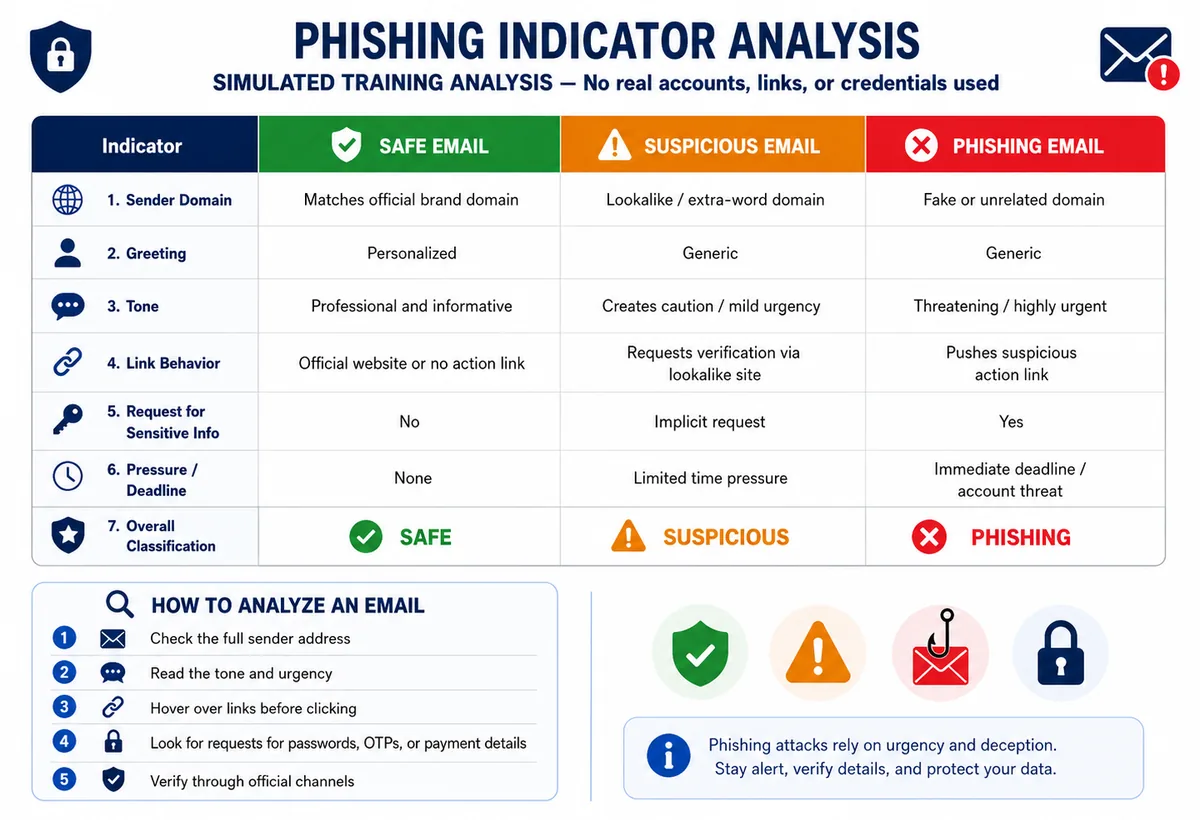
Created a presentation and PDF training module with visual examples.
Awareness
Phishing awareness training
Turn awareness into everyday habits.
A training module that turns phishing red flags into everyday security habits, with a knowledge-check quiz.
Good evening. Welcome to sir’s home lab. I’ll be your guide. We’ll start with sir, then open a few of the more interesting files.